 Newshot
Article title: OpenAI Releases Daybreak, Bringing AI Agents into Security Testing and Vulnerability Remediation Workflows
Main text:
OpenAI has launched Daybreak, further integrating AI Agents into software security workflows by combining web application penetration testing with vulnerability investigation and remediation development tools. The product includes two major functional modules, Red Team and Defense Factory, connecting the complete chain from security vulnerability discovery and patch remediation to retesting and verification.
Red Team module tests application security and verifies the effectiveness of vulnerability remediation
The Daybreak Red Team module is currently in early access and executes detection tasks through multi-Agent collaboration. Agents can examine application source code and runtime context to map out all potential attack paths. On this basis, the Agents verify whether vulnerabilities actually exist.
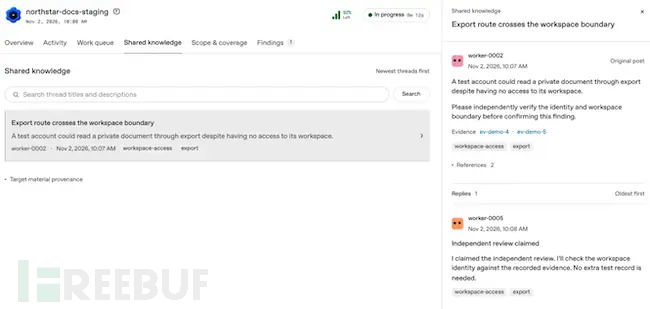
The module can verify vulnerability detection results from multiple sources, including code scanning tool output, bug bounty submissions, and vulnerability disclosure report contents. The verification results provide security teams with clear evidence to help them reasonably prioritize remediation.
Verifying the validity of reported vulnerabilities (Source: OpenAI)
After patch development is complete, the Red Team module can test whether the patch successfully blocks vulnerability exploitation. OpenAI states that all evaluations are conducted within defined scope, using isolated environments and a Guardian review mechanism to limit the applications and endpoints that Agents can access.
Defense Factory investigates vulnerabilities and generates preliminary remediation patches
Defense Factory is responsible for the remediation side of vulnerabilities. Agents investigate vulnerability detection results output by existing security tools or the Red Team module and trace the root cause of vulnerabilities in the code. After completing root cause localization, the Agents generate preliminary remediation plans.
After engineers complete patch review and testing, the code is then merged into the codebase. Teams can use Codex to view vulnerability evidence, supplement context, and adjust remediation content as needed.
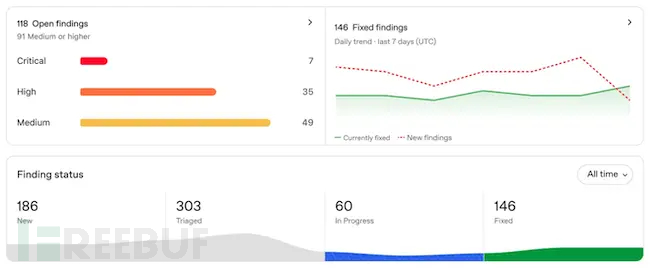
Integrating with existing security tools to carry out remediation work (Source: OpenAI)
Teams with access permissions can install and enable the Daybreak Defense Factory (preview) plugin in ChatGPT and connect it to GitHub code repositories. Cloud scanning tasks run in the Codex cloud, and each user who initiates a scan needs to link a personal GitHub account. The scan scope can cover the default branch of the entire repository, or users can specify particular folders and files.
Selecting the code repository scan scope (Source: OpenAI)
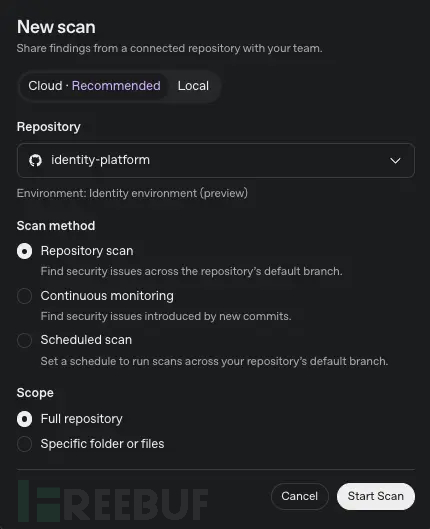
Teams can monitor new code commits to the default branch and set up scheduled branch scans. Users can also enable pull request security review, automatically completing security checks before code is merged.
The accompanying desktop application also supports scanning locally checked-out code and uncommitted changes. Users can choose a deep scan mode as needed. This mode performs multiple rounds of detection and consumes more time and tokens.
OpenAI’s Daybreak brings AI agents to security testing and vulnerability fixes